OVERALL RATINGS
INSTALLS
1
SUPPORT
- Partner Supported
TRUST SIGNALS
Key highlights of the appPermission audit for Jira: see who can access which projects and why, diff snapshots, and sign off access reviews as evidence
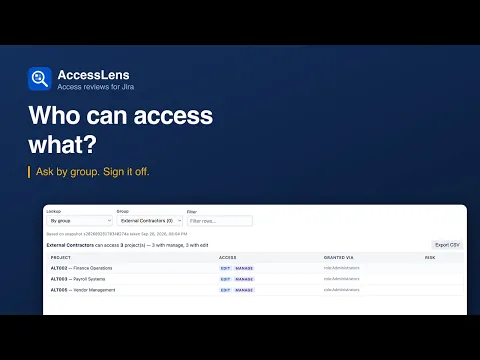
Ask by group, not by project
Jira answers “who can see this project”. AccessLens answers what auditors actually ask: which projects can this group reach, at what level, and how the access was granted.
See what changed between two dates
Snapshot the whole site on a schedule or on demand, then compare any two. Access granted, revoked, projects added or removed, membership changes — itemised, and exportable as CSV.
Sign-off that freezes into evidence
Walk a review project by project, confirm or flag each one with a note, then sign it off. The record freezes against the snapshot it was decided on and exports as an evidence pack.
Supporting media
More details
BUILT FOR COMPLIANCE BUYERS
AccessLens is zero-egress by architecture: its Forge manifest declares no external permissions, which Atlassian enforces at the platform level. Permission data never leaves your Atlassian tenant — no vendor server to trust, nothing to add to your security review. Carries the Runs on Atlassian badge.
TRANSPARENT SECURITY POSTURE
• Security policy: https://keelapps.app/security/ — vulnerabilities acknowledged within 3 working days, confirmed or disputed within 10
• Privacy policy: https://keelapps.app/accesslens/privacy/ — what is stored and where, in plain language
HONEST ABOUT LIMITS
Where the user directory refuses group-member reads, group-level lookup stays complete and user-level lookup is clearly marked partial. The app says so when it cannot see something.
SUPPORT: keelapps.atlassian.net/helpcenter/support · support@keelapps.atlassian.net
LANGUAGES: English
FREE for sites with 10 users or fewer, full functionality.
Resources
App documentation
Comprehensive set of documentation from the partner on how this app works
Privacy and Security
Privacy policy
Atlassian's privacy policy is not applicable to the use of this app. Please refer to the privacy policy provided by this app's partner.
Partner privacy policySecurity program
This app is not part of the Marketplace Bug Bounty program.
Integration permissions
AccessLens — Permission Audit & Access Review for Jira integrates with your Atlassian app
Version information
Version 3.1.0•for Jira Cloud
- Release date
- Sep 28th 2026
- Summary
- Truer access levels, per-person licensed access, sign-offs that stay put
- Details
Found by using AccessLens the way a buyer does.
- Access levels: six Jira permissions were in the wrong class. Archiving and restoring issues read as browse, so a role holding only those looked able to browse the project; Manage sprints and Manage watchers read as manage, so every licensed user looked able to administer every default-scheme project. Existing snapshots are read with the corrected classes.
- By user now counts grants to every licensed user and to anyone, which Jira's default schemes use for Browse projects. It said an admin could reach 1 project when they could browse all 121.
- A project's risk findings list each grant once, with the access it covers, not three identical lines.
- Signed-off reviews are evidence: they keep the rows they showed, cannot be signed again or deleted, and read the same after their snapshot is deleted. A snapshot an open review uses cannot be deleted.
- Decisions and sign-offs record the person's name beside the account id.
- Payment model
- Paid via Atlassian
- License type
- Commercial