OVERALL RATINGS
INSTALLS
1
SUPPORT
- Partner Supported
TRUST SIGNALS
Key highlights of the appWhich spaces can this group reach, which pages are locked, and what changed since last quarter? Snapshot it and sign it off
Answer who can reach what
Confluence's User access report shows admin or user per space. AccessLens shows view, edit or manage for every space, how each was granted, and the restricted pages that name the group or person.
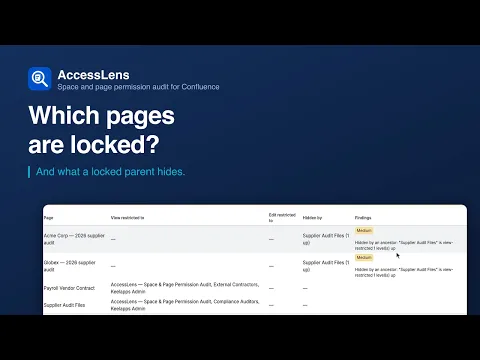
Find locked pages, and what locks them
Confluence lists restricted pages one space at a time, and a page is often hidden by an ancestor, not itself. AccessLens lists both across spaces and flags restrictions that grant nothing: the group cannot see the space.
A snapshot is audit evidence
Capture every current space's permission state on a schedule. Compare two snapshots to see what changed and what could not be compared, then sign the review off with an account id and a server-side UTC timestamp.
Supporting media
More details
Confluence's User access report lists a group's spaces as admin or user. Full permissions are read space by space, pages one at a time for a user or a group (Premium/Enterprise), and none of it keeps last quarter's state. Restricted pages are listed one space at a time, a page is often hidden by an ancestor, not by itself, and a restriction naming a group with no space access grants nothing.
AccessLens reads every current, non-personal space's permissions, expands group membership, reads page restrictions (200 pages per space by default, or all) and what they hide, and keeps it as evidence to cite.
Three constraints are deliberate. At the retention limit it refuses a new snapshot rather than evicting an old one. When it cannot read something it marks the snapshot partial instead of under-reporting. Where a tenant cannot expose anonymous access at all, it says so rather than reporting “none found”.
It declares no external network access, which Forge enforces at the platform level.
Resources
App documentation
Comprehensive set of documentation from the partner on how this app works
Privacy and Security
Privacy policy
Atlassian's privacy policy is not applicable to the use of this app. Please refer to the privacy policy provided by this app's partner.
Partner privacy policySecurity program
This app is not part of the Marketplace Bug Bounty program.
Integration permissions
AccessLens — Space & Page Permission Audit integrates with your Atlassian app
Version information
Version 2.11.0•for Confluence Cloud
- Release date
- Sep 28th 2026
- Summary
- Signed reviews can't be deleted by crafted ids; edit-only pages list again
- Details
Three fixes from a second review of 2.10.0.
A review can only be named by an id AccessLens itself created, so no request can delete the review list and with it the signed reviews. Pages restricted for editing that also sit under a view lock show again in By group and By user; 2.10.0 left them out. And when you compare against a snapshot taken before 2.10.0, a space it could not scan, now listed as added, carries a warning that it may only have failed then.
No new permissions or scopes.
- Payment model
- Paid via Atlassian
- License type
- Commercial