OVERALL RATINGS
INSTALLS
2
SUPPORT
- Partner Supported
TRUST SIGNALS
Key highlights of the appWhich spaces can this group reach, which pages are locked, and what changed since last quarter? Snapshot it and sign it off
Answer who can reach what
Confluence’s User access report stops at admin or user. AccessLens shows view, edit or manage for every space, how each was granted, and the restricted pages that name the group or person.
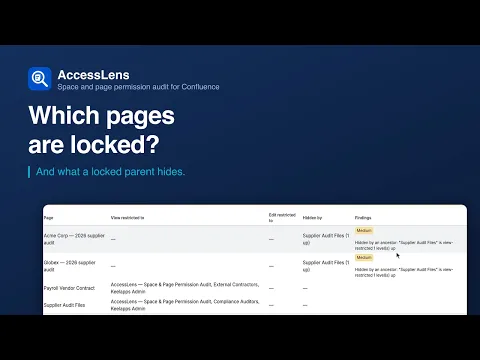
Find every locked page, and what locks it
Confluence lists restricted pages one space at a time, and a page is often hidden by an ancestor, not by itself. AccessLens finds both, and flags restrictions that grant nothing because the group cannot see the space.
A snapshot is audit evidence
Capture the whole site’s permission state on a schedule. Compare any two snapshots to see exactly what changed, then sign the review off with an Atlassian account id and a server-side UTC timestamp.
Supporting media
More details
Confluence's User access report shows a group's spaces as admin or user, and stops there: not the full permission set, not the restricted pages the group can open (CONFCLOUD-74405), not last quarter. Restricted pages are listed one space at a time, a page is often hidden by an ancestor rather than by itself, and a restriction naming a group with no space access grants nothing.
AccessLens reads every space’s permissions, expands group membership, walks page restrictions and their inheritance, and keeps the result as evidence you can cite.
Three constraints are deliberate. At the retention limit it refuses a new snapshot rather than evicting an old one. When it cannot read something it marks the snapshot partial instead of under-reporting. Where a tenant cannot expose anonymous access at all, it says so rather than reporting “none found”.
It declares no external network access, which Forge enforces at the platform level.
Resources
App documentation
Comprehensive set of documentation from the partner on how this app works
Privacy and Security
Privacy and security questionnaire has been filled by the partner
Privacy policy
Atlassian's privacy policy is not applicable to the use of this app. Please refer to the privacy policy provided by this app's partner.
Partner privacy policySecurity program
This app is not part of the Marketplace Bug Bounty program.
Integration permissions
AccessLens — Space & Page Permission Audit integrates with your Atlassian app
Version information
Version 2.9.0•for Confluence Cloud
- Release date
- Sep 27th 2026
- Summary
- Restricted pages by group or person; signed reviews survive snapshot deletes
- Details
Found by using the app the way a buyer would, and fixed:
- By group and By user list the restricted pages that name the group or person, and whether that lets them in, or what stands in the way.
- “Restriction grants nothing” is judged per member: it no longer flags people who reach the space through another group, and it now fires on role-based sites.
- “All logged-in users” is counted once per space, not twice.
- A signed-off review keeps its own copy of what it showed, so deleting its snapshot no longer empties it, and it cannot be signed again.
- Snapshots and comparisons export as CSV, and reviewers can add a note to each decision.
- The Snapshots and Settings tabs say when the schedule runs next, and when it has stopped at the retention limit.
- Payment model
- Paid via Atlassian
- License type
- Commercial