INSTALLS
No installs yet
SUPPORT
- Partner Supported
TRUST SIGNALS
Key highlights of the appExploited vulnerability? 24 hours to warn ENISA under the Cyber Resilience Act: run the clocks, SBOMs and CSAF advisories in Jira
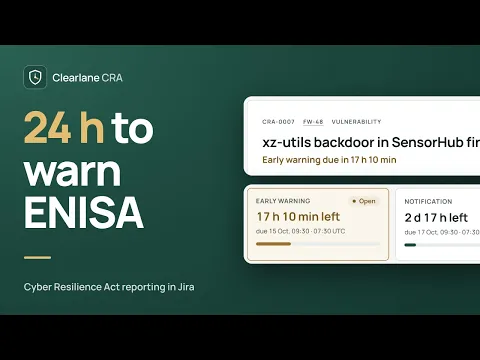
Every Article 14 deadline in view
Vulnerabilities and incidents on any work item, including those your scanners create, with the 24-hour, 72-hour and final-report clocks, and one reminder e-mail a day to each owner.
Ask Rovo about your CRA deadlines
Ask Rovo which Article 14 reports are due next, which cases are open and what is overdue. The Clearlane CRA agent reads with your own Jira permissions and never changes anything.
Find which products ship a component
An SBOM per version, CycloneDX or SPDX. One search covers them all and checks the version range.
Supporting media
More details
Turn the vulnerabilities and incidents already in Jira into the records the Cyber Resilience Act (EU 2024/2847) asks for.
A signed qualification starts the early warning, notification and final report clocks. ENISA Single Reporting Platform fields are ready to paste.
Keep products, versions and support periods; import CycloneDX or SPDX SBOMs and find which versions ship a component.
For your PSIRT: the fix, a CSAF 2.0 advisory and a PDF evidence file. Helps meet Article 14 and Annex I Part II. English, French, German. Runs on Atlassian: your data stays in your Atlassian site.
Pairs with Clearlane Breach & Incident Reporting (NIS2). CRA mapping and OQ scripts: clearlaneapps.com/validation. Maxime Ragionieri answers in writing within two business days.
Auf Deutsch: Cyberresilienz-Verordnung (EU) 2024/2847 in Jira – ausgenutzte Schwachstellen und schwere Sicherheitsvorfälle einstufen, Fristen für Frühwarnung, Meldung und Abschlussbericht, SBOM je Version, CSAF-Sicherheitshinweise.
Resources
App documentation
Comprehensive set of documentation from the partner on how this app works
Privacy and Security
Privacy and security questionnaire has been filled by the partner
Privacy policy
Atlassian's privacy policy is not applicable to the use of this app. Please refer to the privacy policy provided by this app's partner.
Partner privacy policySecurity program
This app is not part of the Marketplace Bug Bounty program.
Integration permissions
Clearlane CRA – Cyber Resilience Act & SBOM for Jira integrates with your Atlassian app
Version information
Version 3.17.0•for Jira Cloud
- Release date
- Oct 30th 2026
- Summary
- Sturdier internal locks and safer case moves
- Details
Sturdier internal locks: an interrupted save no longer holds up the next one or the hourly reminders. A case whose Jira work item was deleted now moves only to a work item of the same project and under the same security level, and the former work item no longer points to the case after a move. A deletion event that arrives while the case is being saved is no longer lost. Reviewed and tested by Clearlane before release. Validation impact: none (case records, signatures, deadlines and evidence files work as before). Enjoying Clearlane CRA? A short review helps other teams find it.
- Payment model
- Paid via Atlassian
- License type
- Commercial