OVERALL RATINGS
INSTALLS
54
SUPPORT
- Partner Supported
TRUST SIGNALS
Key highlights of the appSecurity scanner for leaked credentials: finds and redacts passwords, API keys and tokens in Jira issues and comments
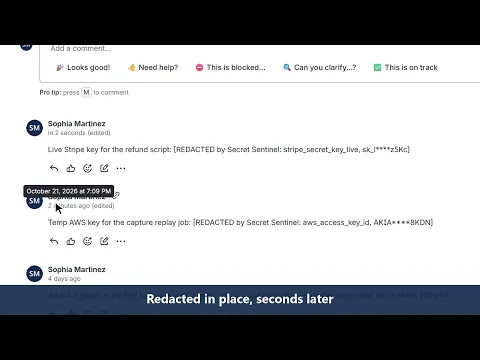
Redacted the moment it is posted
When someone pastes a key into a summary, description or comment, it is replaced by a marker that names the type and shows only its first and last characters. Formatting stays intact.
A security incident for every real leak
Open a work item in your security project with priority, assignee and labels — where the leak was and which types, never the secret itself. Rules per credential type and severity.
Tuned to your organization
Severity per credential type, which types open incidents, excluded projects and safe values. Personal data — card numbers, IBANs, US SSNs — stays off until you turn it on. Advanced adds your own patterns and a report.
Supporting media
Editions
This app offers two different editions - Standard and Advanced. You can start a free trial of either edition, and change your edition anytime during or after the trial.
Standard
Onboard your team and scale fast
Includes:
Automatic secret detection & redaction
Broad secret type coverage
Security incident escalation
Severity & escalation rules
Per-value allowlist
Advanced
Unlock the full range of app features
Everything from Standard, plus:
Custom regex detection rules
Compliance dashboard
More details
- Scans issue summaries, descriptions and comments (also edited ones) when they are created or changed
- 50+ credential types via secretlint rules: AWS, GCP and private keys, GitHub/GitLab, Slack, Stripe, AI services, database URLs, plus password=/token=/api_key= assignments and JWTs
- Personal data, off until you turn it on: card numbers (Luhn-checked), IBANs, US SSNs
- Redacts in place; only first/last 4 characters shown; formatting, tables and code blocks kept
- Severity High / Medium / Low per type; optional Jira security incidents; exclude projects
- Ignored values stored as SHA-256 only
- Advanced: custom RE2 patterns, a report with the findings log (masks only)
Get started: install — scanning starts at once. Jira settings → Apps → Secret Sentinel → Rules to pick types and incidents.
Redaction changes the current version; Jira keeps history — rotate any leaked credential. Runs on Atlassian Forge: everything stays inside your Atlassian site, no external calls.
Resources
App documentation
Comprehensive set of documentation from the partner on how this app works
Privacy and Security
Privacy and security questionnaire has been filled by the partner
Privacy policy
Atlassian's privacy policy is not applicable to the use of this app. Please refer to the privacy policy provided by this app's partner.
Partner privacy policySecurity program
This app is not part of the Marketplace Bug Bounty program.
Integration permissions
Secret Sentinel: Password & API Key Leak Scanner for Jira integrates with your Atlassian app
Version information
Version 2.11.0•for Jira Cloud
- Release date
- Nov 1st 2026
- Summary
- Minor version update
- Details
Minor version update
- Payment model
- Paid via Atlassian
- License type
- Commercial